The Essential Eight explained for business: a practical security guide
Australia’s Essential Eight, also called Essential 8 or E8, gives Australian businesses a practical baseline for reducing common cyber security risks. It focuses on controls that limit the impact of stolen credentials, malware, unpatched systems and unauthorised access.
The Essential Eight helps businesses prevent common cyber threats and reduce the damage when an attack succeeds. This guide explains what each control does, how maturity levels apply and how organisations can turn government guidance into workable security measures.
Key takeaways
- The Essential Eight targets common cyber threats.
- Each control supports practical risk reduction.
- Maturity targets guide security improvements.
What the framework protects against
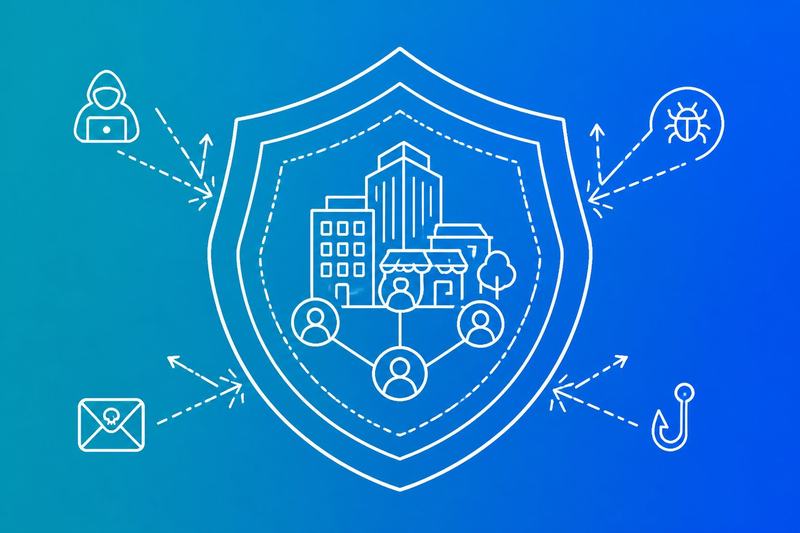
The Essential Eight targets common ways attackers gain access, execute malicious code, steal credentials and disrupt operations. It helps businesses reduce exposure before an incident reaches systems, staff or customers.
The role of ASD, ACSC and the Australian Signals Directorate
The Australian Signals Directorate (ASD) is an Australian Government agency responsible for foreign signals intelligence, cyber security and offensive cyber operations. Its Australian Cyber Security Centre (ACSC) provides cyber security guidance, threat information and incident support for Australian organisations.
ASD publishes the Strategies to Mitigate Cyber Security Incidents, commonly known as the Essential Eight. The framework converts practical controls into eight mitigation strategies covering application control, patching, restricting Microsoft Office macros, user application hardening, restricting administrative privileges, operating system patching, multi-factor authentication and regular backups.
The Essential Eight does not guarantee that a business will prevent every cyber attack. It gives operators a prioritised baseline for reducing the likelihood and impact of common cyber security incidents. Businesses still need to assess their systems, suppliers, data and recovery requirements against their own cyber risk.
Common attack paths: phishing, malware and ransomware
Phishing can trick a worker into opening a malicious attachment, visiting a fraudulent website or disclosing a password. Stolen credentials can support business email compromise, unauthorised access and credential stuffing, particularly when staff reuse passwords across services.
Malware can exploit unpatched operating systems, applications or browsers. Application control can block unauthorised executables, while patching and user application hardening reduce opportunities for malicious code to run. Restricting administrative privileges limits what malware can change after it reaches a device.
Ransomware can encrypt files, interrupt operations and threaten the disclosure of stolen data. Multi-factor authentication helps protect exposed services and privileged accounts, although it does not replace patching or access controls. Backups must remain separate from ordinary user access and undergo restoration testing, otherwise a business may discover that recovery fails during an incident.
Where the Essential Eight fits within cyber risk management
The Essential Eight forms part of a wider cyber risk management programme. It addresses endpoint compromise, identity abuse, malicious code and recovery, but it does not replace governance, asset management, network security, supplier assurance, security monitoring or an incident response plan.
Operators should map each mitigation strategy to business assets and attack paths. They should identify which systems hold sensitive information, which services face the internet, which accounts have privileged access and which processes depend on timely recovery.
Implementation should include defined ownership, technical standards and evidence of operation. Useful checks include reviewing patch age, testing multi-factor authentication coverage, examining application control events, confirming macro restrictions and restoring files from backups.
The Essential Eight maturity model helps a business measure progress against increasing levels of resistance to common attacks. Risk owners should record exceptions, assess their effect and apply compensating mitigation strategies where a control cannot operate as specified.
The eight security controls in practice

These controls reduce the routes attackers commonly use to enter systems, gain higher privileges and disrupt operations. Effective implementation depends on approved software, timely patching, hardened user applications, controlled administration, strong authentication and tested backups.
Application control and approved software
Application control allows only authorised software to run on business devices. It prevents malware, unauthorised tools and altered executables from starting, even when a user opens a malicious attachment or visits a compromised website.
The organisation should maintain an approved software list with the product name, publisher, version and business owner. It should block unapproved executables, scripts, installers and portable applications, including those launched from temporary folders or user-writable locations.
Controls should cover Windows, macOS and Linux where those systems are used. They should also address interpreters and scripting tools such as PowerShell, Python and JavaScript runtimes. IT teams should review exceptions, remove unused software and record approval decisions.
Application control must not rely only on file names. Attackers can rename files or use legitimate tools for harmful purposes, so rules should use trusted publishers, code signing, file hashes or managed deployment paths where practical.
Patching applications and operating systems
Unpatched applications and operating systems give attackers known weaknesses to exploit. A malicious website, email attachment or stolen account can become an entry point when a device runs an outdated browser, document viewer or operating system.
The organisation should maintain an inventory of Windows, macOS and Linux devices, installed applications and supported versions. It should prioritise internet-facing software, browsers, remote access tools, email clients, Microsoft Office, Java and other products that process untrusted content.
Patch compliance should show which devices received each update, which failed and why. IT teams should test important patches, deploy them through central management and set escalation rules for devices that remain non-compliant. Unsupported operating systems and applications should be removed, upgraded or isolated.
Teams should apply security updates promptly according to the organisation's risk assessment. They should also verify that updates completed successfully, because a reported deployment does not prove that a device installed or activated the patch.
Office macros and user application hardening
Microsoft Office macros can run code when a user opens a document. Attackers may use them to download malware, steal data or provide access to other systems, particularly when they send convincing invoices or business documents.
Organisations should configure Microsoft Office macro settings to block macros from files obtained from the internet. They should permit digitally signed macros only when a defined business process requires them, and they should store trusted templates in controlled locations.
IT teams should review OLE and ActiveX behaviour, disable unnecessary features and prevent Office applications from creating child processes where security tooling supports that control. They should remove obsolete components such as Flash and restrict Java if no approved business use remains.
User application hardening should cover web browsers, PDF readers, collaboration clients and document viewers. It should disable unnecessary extensions, restrict downloads and prevent automatic execution of active content. Users should not receive instructions to weaken these settings to view routine business material.
Administrative access and multi-factor authentication
Excessive administrative privileges allow a compromised account to change security settings, install software or move across systems. A standard user account should handle routine work, while a separate admin account should perform approved administrative tasks.
The organisation should restrict administrative privileges through role-based access, time-limited elevation and regular access reviews. It should remove local administrator rights where they are not required, block shared admin accounts and record privileged activity.
Privileged access workstations, or PAWs, should provide a dedicated environment for high-risk administration. Admins should avoid browsing the web, reading email or opening untrusted documents from a PAW. Conditional access should restrict privileged sign-ins by device status, location and risk.
Multi-factor authentication should protect admin accounts, the workspace platform, remote access and other exposed services. Phishing-resistant MFA, such as FIDO2 security keys, provides stronger protection than codes sent by SMS or email. Recovery methods require the same level of control as primary authentication.
Backups and recovery testing
Ransomware and destructive attacks can encrypt production data, delete online backups or compromise backup credentials. Hardware failure, human error and cloud service incidents can also remove access to important records without warning.
The organisation should take regular backups of critical data, configurations and essential applications. It should keep copies separated from ordinary administrator accounts and production networks, with access controls that prevent attackers from modifying or deleting every copy.
Backup schedules should reflect how much data the business can afford to lose. Recovery plans should identify system priorities, responsible staff, dependencies and communication routes. They should cover the workspace platform and other cloud services where the provider does not meet the organisation's recovery needs.
Recovery testing should restore files and complete systems in a controlled environment. Tests should confirm that backups are usable, credentials work, applications start and data meets business requirements. Teams should record failures, correct them and repeat tests after major system changes.
Choosing and reaching a maturity target
The Essential Eight maturity model helps an organisation measure how consistently it applies eight security controls and identify the target maturity level required for its risk profile. A reliable assessment, documented exceptions and effective compensating controls help turn the target into a practical security baseline.
How the Essential Eight maturity model is scored
The Essential Eight maturity model scores each mitigation separately from ML0 to ML3. An organisation’s result should reflect the weakest relevant requirement, not an average that hides a critical gap.
Assessors examine whether controls exist, apply to the correct systems and operate as intended. Evidence can include configuration records, privileged access reviews, patch reports, backup restoration tests, application control policies and phishing-resistant authentication settings.
The assessment should cover the scope defined by the organisation, such as internet-facing services, user endpoints, servers, cloud services and administrative accounts. If a control does not meet a requirement, the organisation should record the gap rather than mark the control as compliant.
A target maturity level should reflect business impact, threat exposure, legal obligations and customer commitments. A higher target does not remove the need to test individual security controls.
Maturity levels 0 to 3
The Essential Eight maturity levels describe increasing resistance to common attack methods:
Level Meaning ML0 The organisation has weaknesses that leave it exposed to common attacks. Controls may be absent, inconsistent or poorly maintained. ML1 The organisation addresses common threats with a defined set of controls, although gaps and exceptions may remain. ML2 Controls provide stronger protection against adversaries who use more targeted techniques and exploit weaknesses in administration or configuration. ML3 Controls are mature, consistently enforced and designed to resist highly capable attackers, including those who target privileged access and security processes.An organisation should set a target maturity level for each mitigation, then assign ownership and a due date. Its security baseline should state the required configuration, approved exceptions and evidence needed to demonstrate implementation.
Reaching maturity level 1 does not automatically satisfy every customer or regulatory requirement. Compliance depends on the applicable scope, control wording, evidence and any additional obligations.
Running an Essential Eight assessment
An Essential Eight assessment should begin with a defined scope and an accurate asset inventory. The organisation should identify operating systems, applications, identities, cloud services, backup platforms and devices that store or access sensitive information.
The assessment team should map each mitigation to specific technical controls and operating procedures. It should test actual settings rather than rely only on policy documents. For example, it can sample patch records, inspect multifactor authentication coverage, review administrator accounts and confirm that backups can be restored.
The Essential Eight assessment process guide can help structure evidence collection, interviews, sampling and gap recording. Each finding should state the affected asset or process, the unmet requirement, the risk, the owner and the remediation date.
Independent review can improve confidence when the assessment supports customer assurance or formal compliance. The organisation should reassess after major system changes and at planned intervals, because controls can drift when systems, suppliers or user populations change.
Closing gaps with compensating controls
A gap can leave an exposed service, account or device vulnerable before the organisation completes its planned Essential Eight implementation. The owner should first remove the exposure, apply the required control or isolate the affected asset.
A compensating control can reduce risk when the prescribed control cannot yet be implemented. Examples include network isolation, application allow-listing, restricted administrator access, stronger monitoring, temporary service removal or additional approval for sensitive actions.
The alternative control should address the same threat and document its limits. It should identify the affected asset, risk owner, expiry date, monitoring method and replacement plan. A compensating control should not become a permanent exception without formal risk acceptance.
The organisation should test whether the control works in practice. If a legacy system cannot support a required security setting, restricted network access and closely monitored administrative sessions may reduce exposure, but they may not provide the same protection as the required control. Reassessment should confirm when the gap closes.
Governance, contracts and the next steps
Government contracts, security obligations and customer assurance requirements can determine how an organisation applies the Essential Eight. Clear ownership, documented controls and repeatable evidence help prevent a cyber incident from becoming a contractual, regulatory or operational failure.
Government and defence requirements
Australian Government entities and Commonwealth entities must consider the Protective Security Policy Framework (PSPF) when managing security risks. The PSPF covers governance, information security, personnel security and physical security. It may apply directly to an entity or flow through a contract, grant or service arrangement.
Defence industry suppliers may also need to meet requirements under the Defence Industry Security Program (DISP). DISP membership and contract conditions can require controls for personnel, physical sites, information and cyber security. A supplier should confirm the exact obligations for each contract rather than assuming that Essential Eight maturity alone satisfies them.
Critical infrastructure providers face additional obligations under the Security of Critical Infrastructure Act 2018 and related rules. Contract teams should record requirements for incident reporting, access control, subcontractors, data location and audit rights. They should also identify who must notify an Australian Government entity, Defence or another regulator when an incident affects a customer service.
Aligning with ISO 27001, NIST and the ISM
The Essential Eight addresses specific attack prevention and recovery measures. ISO 27001 provides a broader information security management system, including governance, risk treatment, internal review and continual improvement. An organisation can use ISO 27001 to manage the system around its Essential Eight controls, but certification does not automatically prove compliance with the Essential Eight.
The NIST Cybersecurity Framework helps organisations structure activities around identifying, protecting, detecting, responding and recovering. The Australian Government’s Information Security Manual (ISM) provides Australian guidance for protecting systems and information. Teams should map requirements rather than duplicate documents.
A practical control register can link each requirement to its owner, system, procedure, test method and evidence. This exposes gaps such as strong technical settings without a tested recovery process, or a policy that lacks operational enforcement.
Evidence, assurance and ongoing review
Weak evidence can delay a tender, renewal or incident investigation. It can also conceal control failure. Organisations should retain dated records such as vulnerability scan results, patch reports, application control policies, multi-factor authentication coverage, backup restoration tests and administrator access reviews.
The evidence should show scope, result, exceptions and corrective action. A dashboard can track overdue patches, unsupported software, failed backups and unresolved privileged access findings. It should distinguish a control that exists from one that works consistently.
Independent assurance may include internal audit, penetration testing, supplier reviews or an external assessment. Cyber insurers may request evidence of multi-factor authentication, backups, endpoint protection and incident response. Insurance does not replace risk management, and inaccurate answers can create coverage issues.
Preparing for the Essentials Series
The Essentials series extends beyond the original Essential Eight focus. Organisations should monitor official Australian Government guidance and assess how changes affect policy, contracts, technology and supplier management. They should avoid treating a future requirement as complete until its scope and assessment method are clear.
Essentials for enterprise IT may require larger organisations to show stronger governance, risk management and assurance across complex environments. Teams should prepare by maintaining an accurate asset inventory, assigning control owners and recording exceptions with approved expiry dates.
The next steps should include a contract review, a gap assessment against the current Essential Eight maturity target and a remediation plan with accountable owners. Management should fund priorities based on likely harm, including loss of sensitive information, service interruption, safety impacts and notification duties. Suppliers should receive measurable security requirements and face review when their access, systems or risk profile changes.
Frequently asked questions
The Essential Eight combines eight practical controls with maturity levels that help businesses reduce common attack paths. An assessment can show control gaps, prioritise remediation and support evidence-based risk decisions.
What is the Essential Eight and why does it matter for businesses?
The Essential Eight is a cyber security framework developed by the Australian Signals Directorate. It focuses on controls that limit malware execution, restrict account misuse, reduce software vulnerabilities and support recovery after an incident.
A business that leaves internet-facing software unpatched, permits unrestricted macros or uses weak administrator controls gives attackers more opportunities. Applying the Essential Eight reduces those opportunities, although it does not remove every cyber security risk.
What are the eight mitigation strategies in the Essential Eight framework?
The eight strategies are:
- Application control - permits only approved applications, scripts, libraries and installers to run.
- Patch applications - fixes vulnerabilities in user applications such as browsers, document readers and email clients.
- Configure Microsoft Office macro settings - restricts macros and allows them only from trusted locations or trusted publishers where justified.
- User application hardening - disables risky features such as unnecessary browser components and Office content that can execute code.
- Restrict administrative privileges - limits administrator access and prevents standard users from performing privileged tasks.
- Patch operating systems - applies security updates to supported operating systems within defined timeframes.
- Multi-factor authentication - requires more than one authentication factor for suitable accounts and services.
- Regular backups - creates, protects and tests backups so the business can restore data and systems after an incident.
What cyber threats does the Essential Eight help to reduce?
Malware can exploit unpatched applications, malicious macros or unsafe browser features. Application control, patching, macro restrictions and application hardening reduce the chance that malicious code will execute.
Stolen passwords can let attackers access email, remote services or administrative functions. Multi-factor authentication and restricted administrative privileges make that access harder to use.
Ransomware can encrypt production data and disrupt operations. Protected, separate and tested backups give the business a recovery option, while patching and application controls can reduce the chance of the initial compromise.
How does the Essential Eight maturity model assess cyber security controls?
The maturity model measures how consistently a business applies the eight strategies. It uses maturity levels from ML1 to ML3, with ML4 representing an advanced level of protection against highly capable threat actors.
At lower levels, controls may address common attacks but leave gaps in coverage, timeliness or enforcement. Higher levels require stronger protection, faster response to vulnerabilities, tighter administrative controls and more reliable evidence that systems meet the intended settings.
The model does not provide a simple pass or fail across every business risk. It assesses specific control outcomes against defined maturity requirements, so a business must identify which systems, users and services fall within scope.
What is an Essential Eight assessment and what does it provide?
An Essential Eight assessment examines the business's systems, configurations, processes and evidence against the framework. It may include configuration reviews, interviews, sample testing, vulnerability records, access reviews and backup restoration evidence.
The resulting report should identify each strategy's maturity level, control weaknesses, affected assets and recommended remediation. It can also record assumptions, exclusions, supporting evidence and residual risks.
An assessment cannot guarantee that a business will avoid a breach. Its value depends on accurate scope, reliable evidence and the business acting on identified gaps.
How can a business implement the Essential Eight controls?
The business should begin by identifying its users, endpoints, servers, cloud services, applications, privileged accounts and critical data. It should then define ownership, scope and target maturity levels based on operational risk and customer obligations.
A practical implementation sequence is:
- Establish an accurate asset inventory and remove unsupported software.
- Apply security updates to operating systems and applications.
- Enforce multi-factor authentication, starting with administrators and remote access.
- Separate administrator accounts from standard user accounts and review privileges.
- Restrict macros, harden browsers and disable unnecessary software features.
- Deploy application control in audit mode, then enforce approved software rules.
- Configure backups with restricted access, separation from production systems and regular restoration tests.
- Collect evidence, measure exceptions and review controls after major system changes.
The business should assign owners to exceptions and set deadlines for remediation. It should also test whether controls work in practice, because a documented policy does not protect systems if configurations, accounts or backups do not match it.