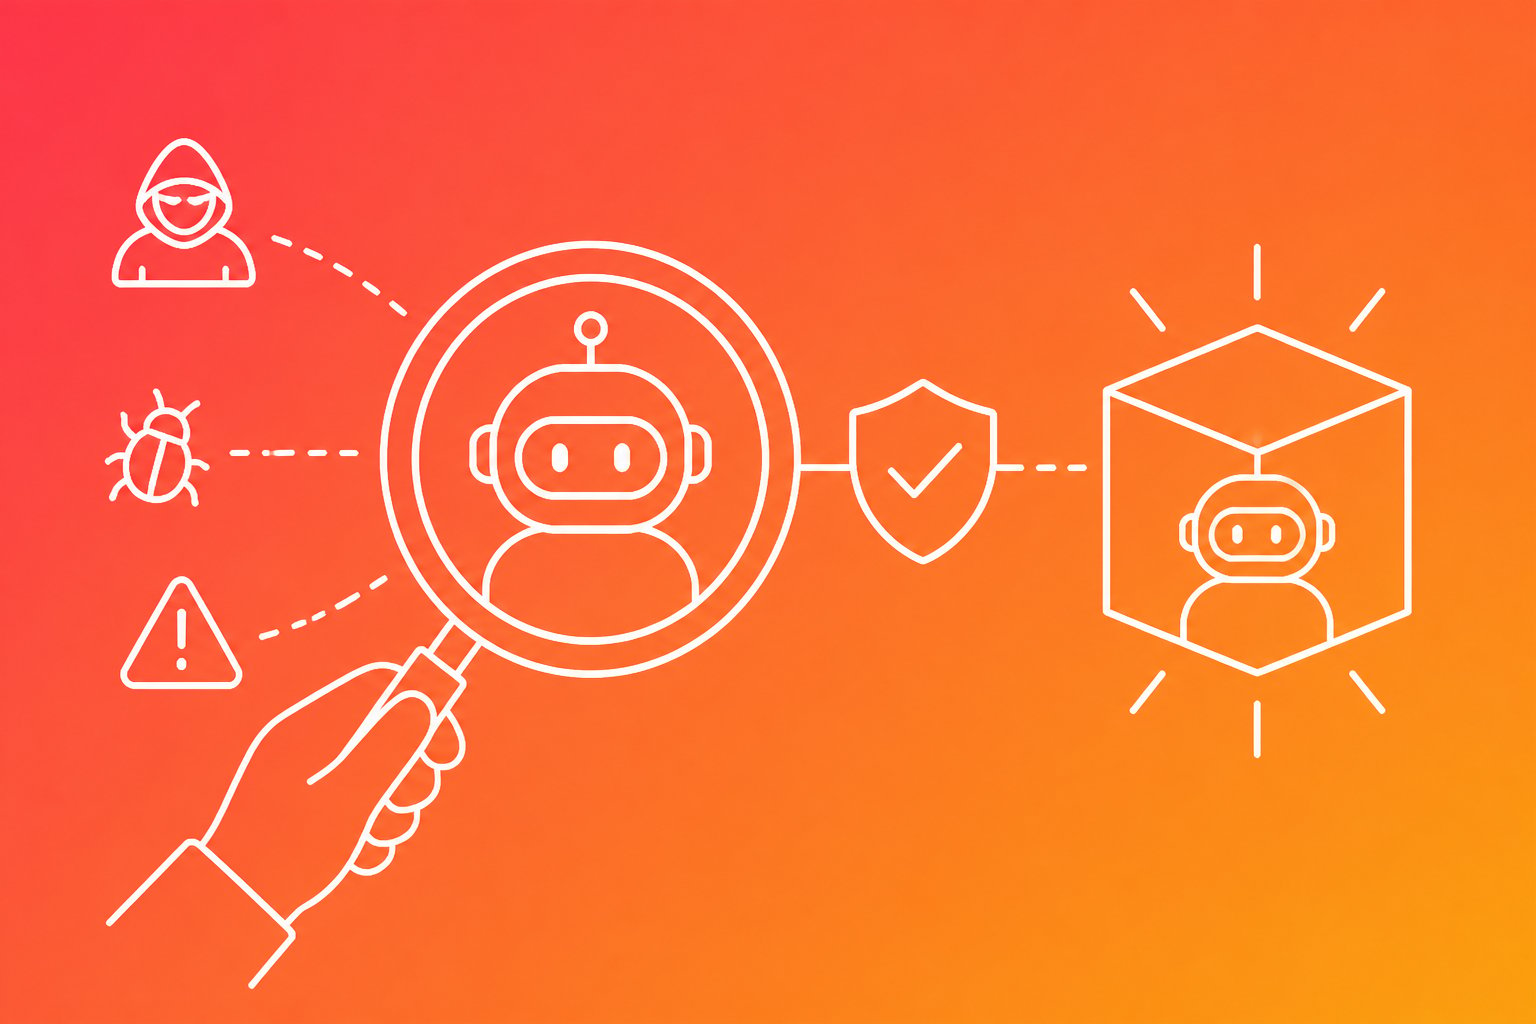
An agent is a program you have handed a little judgement and a lot of reach. The threat model is not exotic. It is the same discipline you would apply to any service, plus one assumption: treat every input it reads as written by someone trying to misuse it.
Map what it can reach
List every tool, credential and data store the agent can touch. That list is your attack surface. Most incidents we have reviewed trace back to a permission that was granted for convenience and never removed.
Assume the prompt is hostile
If the agent reads anything a user or a third party controls, assume that text will try to redirect it. Do not rely on instructions alone to hold the line. Put the boundary in the tools it is allowed to call, so a hijacked prompt still cannot reach what it must not touch.
Write down what it will not do
The most useful artifact is a short list of actions the agent is never permitted to take, enforced outside the model. When something goes wrong, that list is the difference between an odd log line and a headline.